Personal project · Original playbooks · Fall 2026
SOC Incident Response Playbook.
A set of original, practical incident response playbooks for SOC analysts. Each walks through the same eight phases so an analyst can pick up any alert type and know what to do next.
01
Workflow
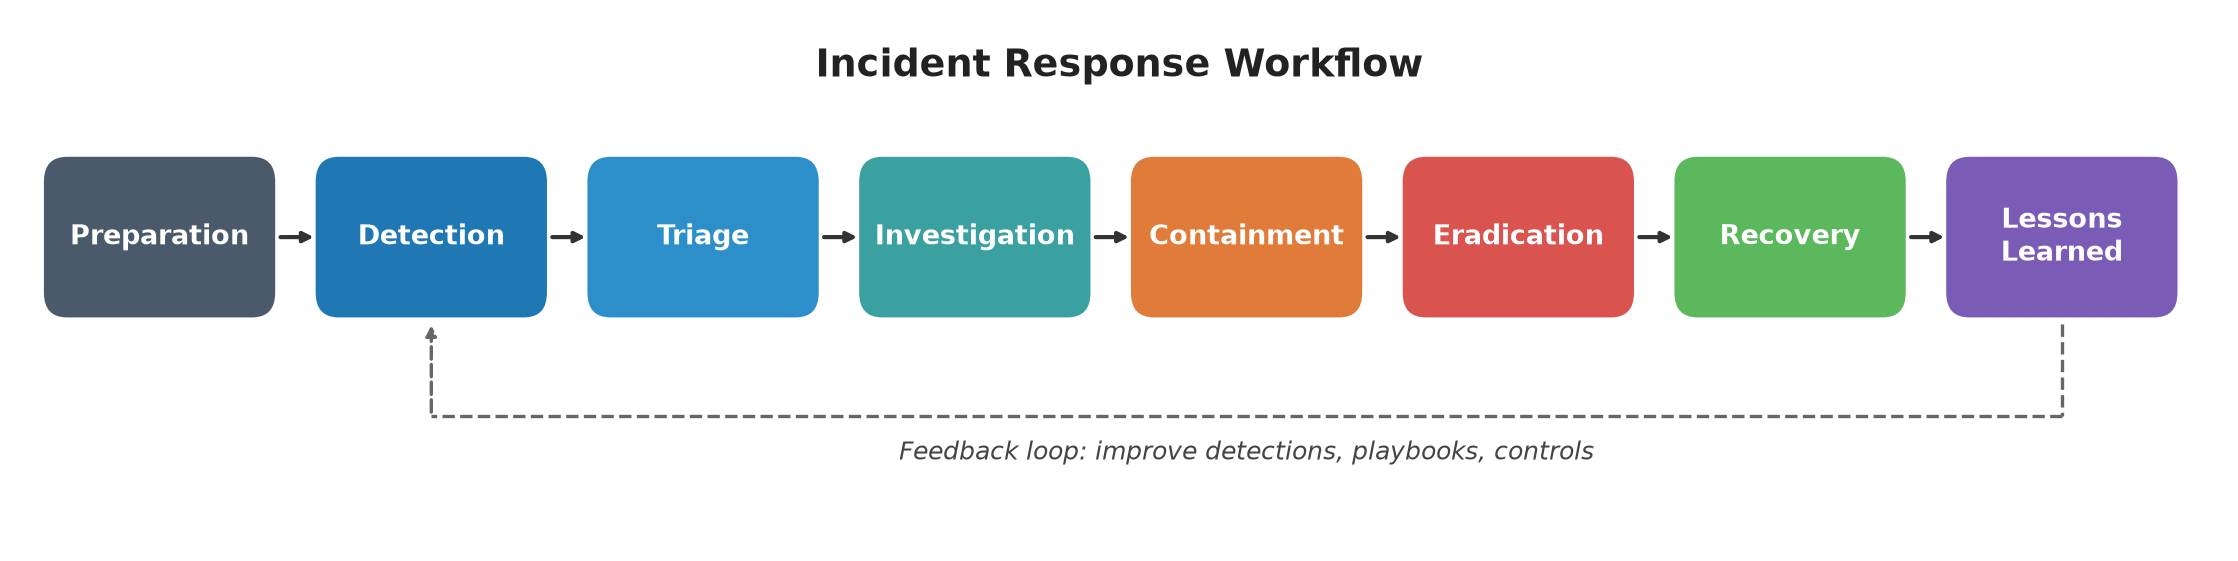
Diagram from the repository. NIST SP 800-61 groups handling into four phases; I split them into eight operational SOC steps so each maps to concrete analyst actions.
02
Scenario
An alert fires. The analyst picks the matching playbook, fills in the standard triage fields (host, user, IP, process, hash, severity, time) on the ticket, works through the phases in order, uses the escalation table to decide when to bring in a senior analyst, and closes with lessons learned that feed back into detections.
03
Playbooks
04
Tools & Frameworks
- NIST SP 800-61
- MITRE ATT&CK
- CISA IR Playbooks (reference)
- Markdown documentation
05
Example: Phishing Investigation Steps
- CollectOriginal message with full headers
- Review headersReturn-Path, Reply-To, Received chain, SPF/DKIM/DMARC
- ExtractURLs, domains, attachments; SHA256 attachments; check reputation without opening
- ScopeSearch mail logs for every recipient of the same sender/subject/URL
- Check exposureProxy/DNS logs for visits; sign-in logs for users who entered credentials
- Look for persistenceNew mailbox forwarding or inbox rules
06
MITRE ATT&CK Coverage
T1566.001/.002SpearphishingPhishingT1574.002DLL Side-LoadingMalwareT1547.001Registry Run KeysMalwareT1053.005Scheduled TaskMalwareT1110.001/.003/.004Brute ForceBrute forceT1486Data Encrypted for ImpactRansomwareT1490Inhibit System RecoveryRansomwareT1078Valid AccountsSeveralT1621MFA Request GenerationSuspicious loginT1550.004Web Session CookieSuspicious loginPartial list. Each playbook has its full mapping in the repo.
07
Evidence
📷Screenshot: add an image of a playbook or the checklist in use
08
What I Learned
- Splitting NIST's four phases into eight concrete steps makes each analyst action clear.
- Recording the same triage fields first makes every alert type easier to hand off and escalate.
- Preparation (logging, detection rules, access rights) decides how fast you can respond.
- Lessons learned should feed straight back into detections and playbooks.